
GRC blogs
Explore our blogs for expert insights, industry updates, and practical guidance
Designed to challenge ways of thinking and help your enterprise excel in GRC.
-
Why employee engagement is critical to your GRC program’s success: key takeaways from Gartner ERAC
Read more: Why employee engagement is critical to your GRC program’s success: key takeaways from Gartner ERACEffective GRC (governance, risk, and compliance) depends on the people across your organization. You can have well-designed, optimized processes supported by sophisticated technology that automates workflows. However, if employees and other stakeholders are not engaged or do not follow those processes, the value is lost. People provide the data, insights, and critical review that make…
-
How to manage risk and resilience using the 5 capitals model
Read more: How to manage risk and resilience using the 5 capitals modelMost organizations still run risk management and resilience planning as separate functions. A 5 capitals model shows why treating them as one builds real business resilience. Key takeaways for this risk and resilience guide Introduction: flipping the risk management coin A few years ago, one UK firm made a small, telling change. Its risk and…
-
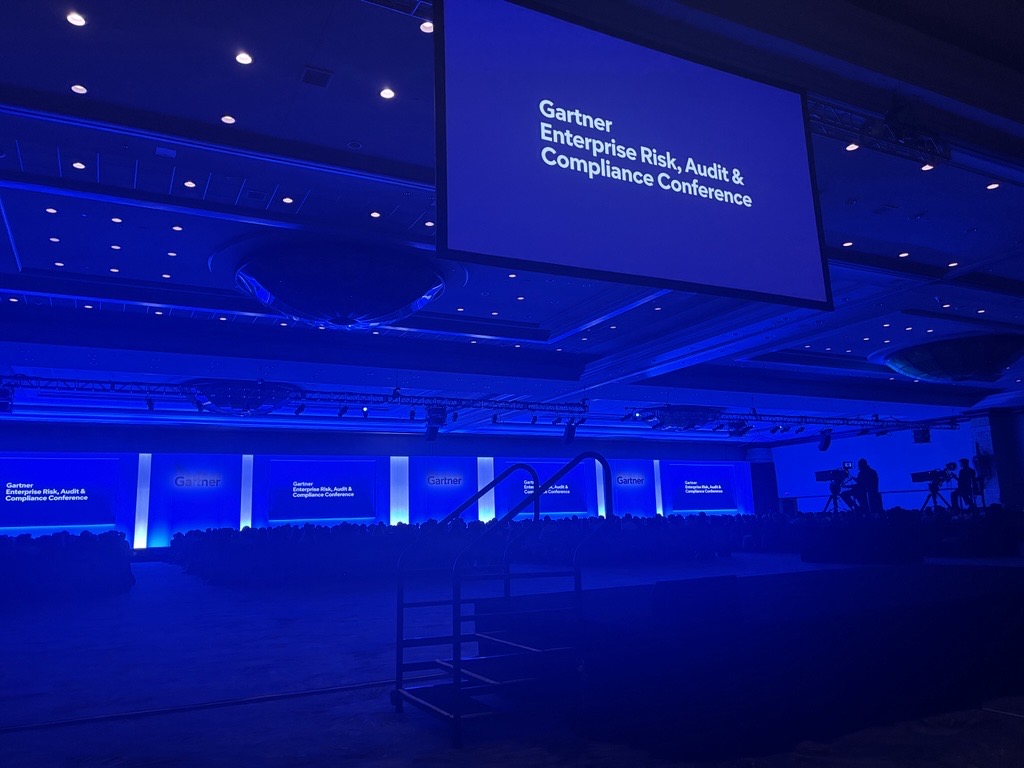
From risk management to business outcomes: what Gartner’s GRC insights mean for risk leaders
Read more: From risk management to business outcomes: what Gartner’s GRC insights mean for risk leadersRisk leaders do not need more information. They need more of the right context. That was one of the clearest themes we took from the 2026, North American, Gartner’s Enterprise Risk, Audit and Compliance Conference. Across sessions the conversation repeatedly came back to a bigger question: how can GRC help organizations make better decisions and…
-
The future of risk, cybersecurity, and due diligence: Key insights from CoreStream GRC’s upcoming industry panels
Read more: The future of risk, cybersecurity, and due diligence: Key insights from CoreStream GRC’s upcoming industry panelsIf there is one theme that has emerged from CoreStream GRC’s news and insights coverage throughout 2026, it’s this: Risk is becoming more interconnected, more technology-driven, and more business-critical than ever before. As preparations begin for Risk Expo Europe 2026 and XapienXchange London 2026, many of the questions dominating boardrooms today are the same issues CoreStream GRC has been tracking throughout the year: The result…
-
There are no new risks, only new combinations: how pre-mortems and digital twins help GRC teams anticipate cascading risks
Read more: There are no new risks, only new combinations: how pre-mortems and digital twins help GRC teams anticipate cascading risksKey takeaways Introduction: when risks combine resilience can suffer When national governments began locking down in spring 2020, few risk registers anywhere carried a line for “global shortage of automotive microchips.” Carmakers, forecasting a pandemic-driven collapse in demand, canceled their orders just as consumer electronics manufacturers absorbed the freed-up capacity to build laptops and games consoles for people stuck at…
-
Spotlight on Women in GRC on value-based internal audit and why business value matters more than findings
Read more: Spotlight on Women in GRC on value-based internal audit and why business value matters more than findingsIn a recent Spotlight on Women in GRC podcast, Lucy Montague sat down with Rachel Paddon, Director of Internal Audit and Risk at Coats Group plc, to discuss the evolution of internal audit, risk-based assurance, and the growing expectation for GRC functions to deliver measurable business value. Having recently expanded her remit from internal audit into enterprise…
-
Beyond the RAG chart: effective GRC reporting at board-level
Read more: Beyond the RAG chart: effective GRC reporting at board-levelKey takeaways Introduction: from static snapshot to compliance story Picture a typical quarterly board pack. The compliance slide shows 98% green, no red flags and no open questions, so the board moves on within a few minutes. Then, months later, a control failure that had in fact been recurring quietly for a year surfaces as a genuine incident, and the first question anyone asks…
-
Health compliance: how to manage HIPAA, HITRUST, AI Governance and Open Payments
Read more: Health compliance: how to manage HIPAA, HITRUST, AI Governance and Open PaymentsKey takeaways for overlapping healthcare compliance requirements in North America Introduction: why is healthcare compliance becoming harder to manage? Healthcare compliance teams are no longer managing one major requirement at a time. They are dealing with HIPAA, HITECH, HITRUST, cyber risk, AI governance, Open Payments, conflict of interest and internal oversight at once. Those expectations…
-
Spotlight on Women in GRC: Sophie Walsh on trust, risk, and the Future of outcome-based GRC
Read more: Spotlight on Women in GRC: Sophie Walsh on trust, risk, and the Future of outcome-based GRCIn a recent Spotlight on Women in GRC podcast, Lucy Montague sat down with Global Director of Trust & Safety, Sophie Walsh, a risk, integrity and compliance leader whose career spans charities, global technology platforms, and some of the most complex risk environments in modern business. From social care and NGOs to digital regulation and e-commerce, Sophie’s work has been guided…
-
Too much faith in frameworks: The governance limits of industry standard certifications
Read more: Too much faith in frameworks: The governance limits of industry standard certificationsKey takeaways Introduction: when GRC certification becomes destination At a recent CoreStream GRC webinar on the modern CISO’s compliance stack, the panel was asked a blunt question: are there any regulations, frameworks or certifications that organizations place too much faith in? Tom Cornelius, founder of the Secure Controls Framework and senior partner at ComplianceForge, didn’t hesitate. He named SOC 2 and ISO 27001 directly, and called the market that…
Ready to speak to our experts?
Discover our case studies
The success stories of flexible intuitive GRC technology
-
CASE STUDY: South Western Railway
Reinventing rail compliance: how South Western Railway kept obligations under control through re-nationalization Contracts change. Ownership changes. Reporting lines change. However, what does not change is the impact risk can have on a business. Obligations must be tracked, updated, evidenced, and reported. And if your Governance, Risk & Compliance (GRC) platform cannot flex with the business change, teams fall back to outdated methods; spreadsheets, inbox chasing and hoping nothing gets missed. South Western Railway…
-
GUIDE: buying a GRC platform
How to choose the right GRC software for your business: A buyer’s guide Buying GRC software is rarely just a software decision. By the time most organizations start reviewing platforms, they are usually already dealing with something more structural: fragmented reporting, unclear ownership, too much manual chasing, weak leadership visibility, and governance activity spread across…
-
CASE STUDY: Pool Re
From constraint to control: how CoreStream GRC transformed risk management at Pool Re About Pool Re Pool Re is the UK’s largest terrorism reinsurer, trusted by over 150 insurers and globally recognized as the leading experts in terrorism risk financing. Their mission is to provide financial protection against the risk of terrorism and, in so…
Ready to upgrade your GRC tech?
Contact the team and request your demo today.
This form may not be visible due to adblockers, or JavaScript not being enabled.