Most organizations are treating the EU AI Act as a standalone compliance project.
That’s a mistake. If your AI systems process personal data, AI compliance doesn’t sit in its own silo. Treating these responsibilities separately risks duplicated work, inconsistent controls and gaps in accountability. Data protection, governance, risk management, audit and compliance all have a role to play.
By December 2027, proactive organizations will have built AI governance into their existing GRC frameworks. While those that separate these obligations will have created more complexity and risk.
“Consider an organization introducing an AI-enabled recruitment tool. The project may involve EU AI Act classification, personal data processing, a data protection impact assessment, supplier due diligence, bias testing, human oversight and ongoing monitoring. Managing each obligation separately creates duplication and blind spots. A connected approach gives risk, privacy, legal and audit teams a shared view of the system, its controls and the evidence required.”
Paul Cadwallader, GRC Strategy Director, CoreStream GRC
The EU AI Act deadline may have moved, but the governance challenge hasn’t. Those who wait until 2027 to start planning will already be behind.
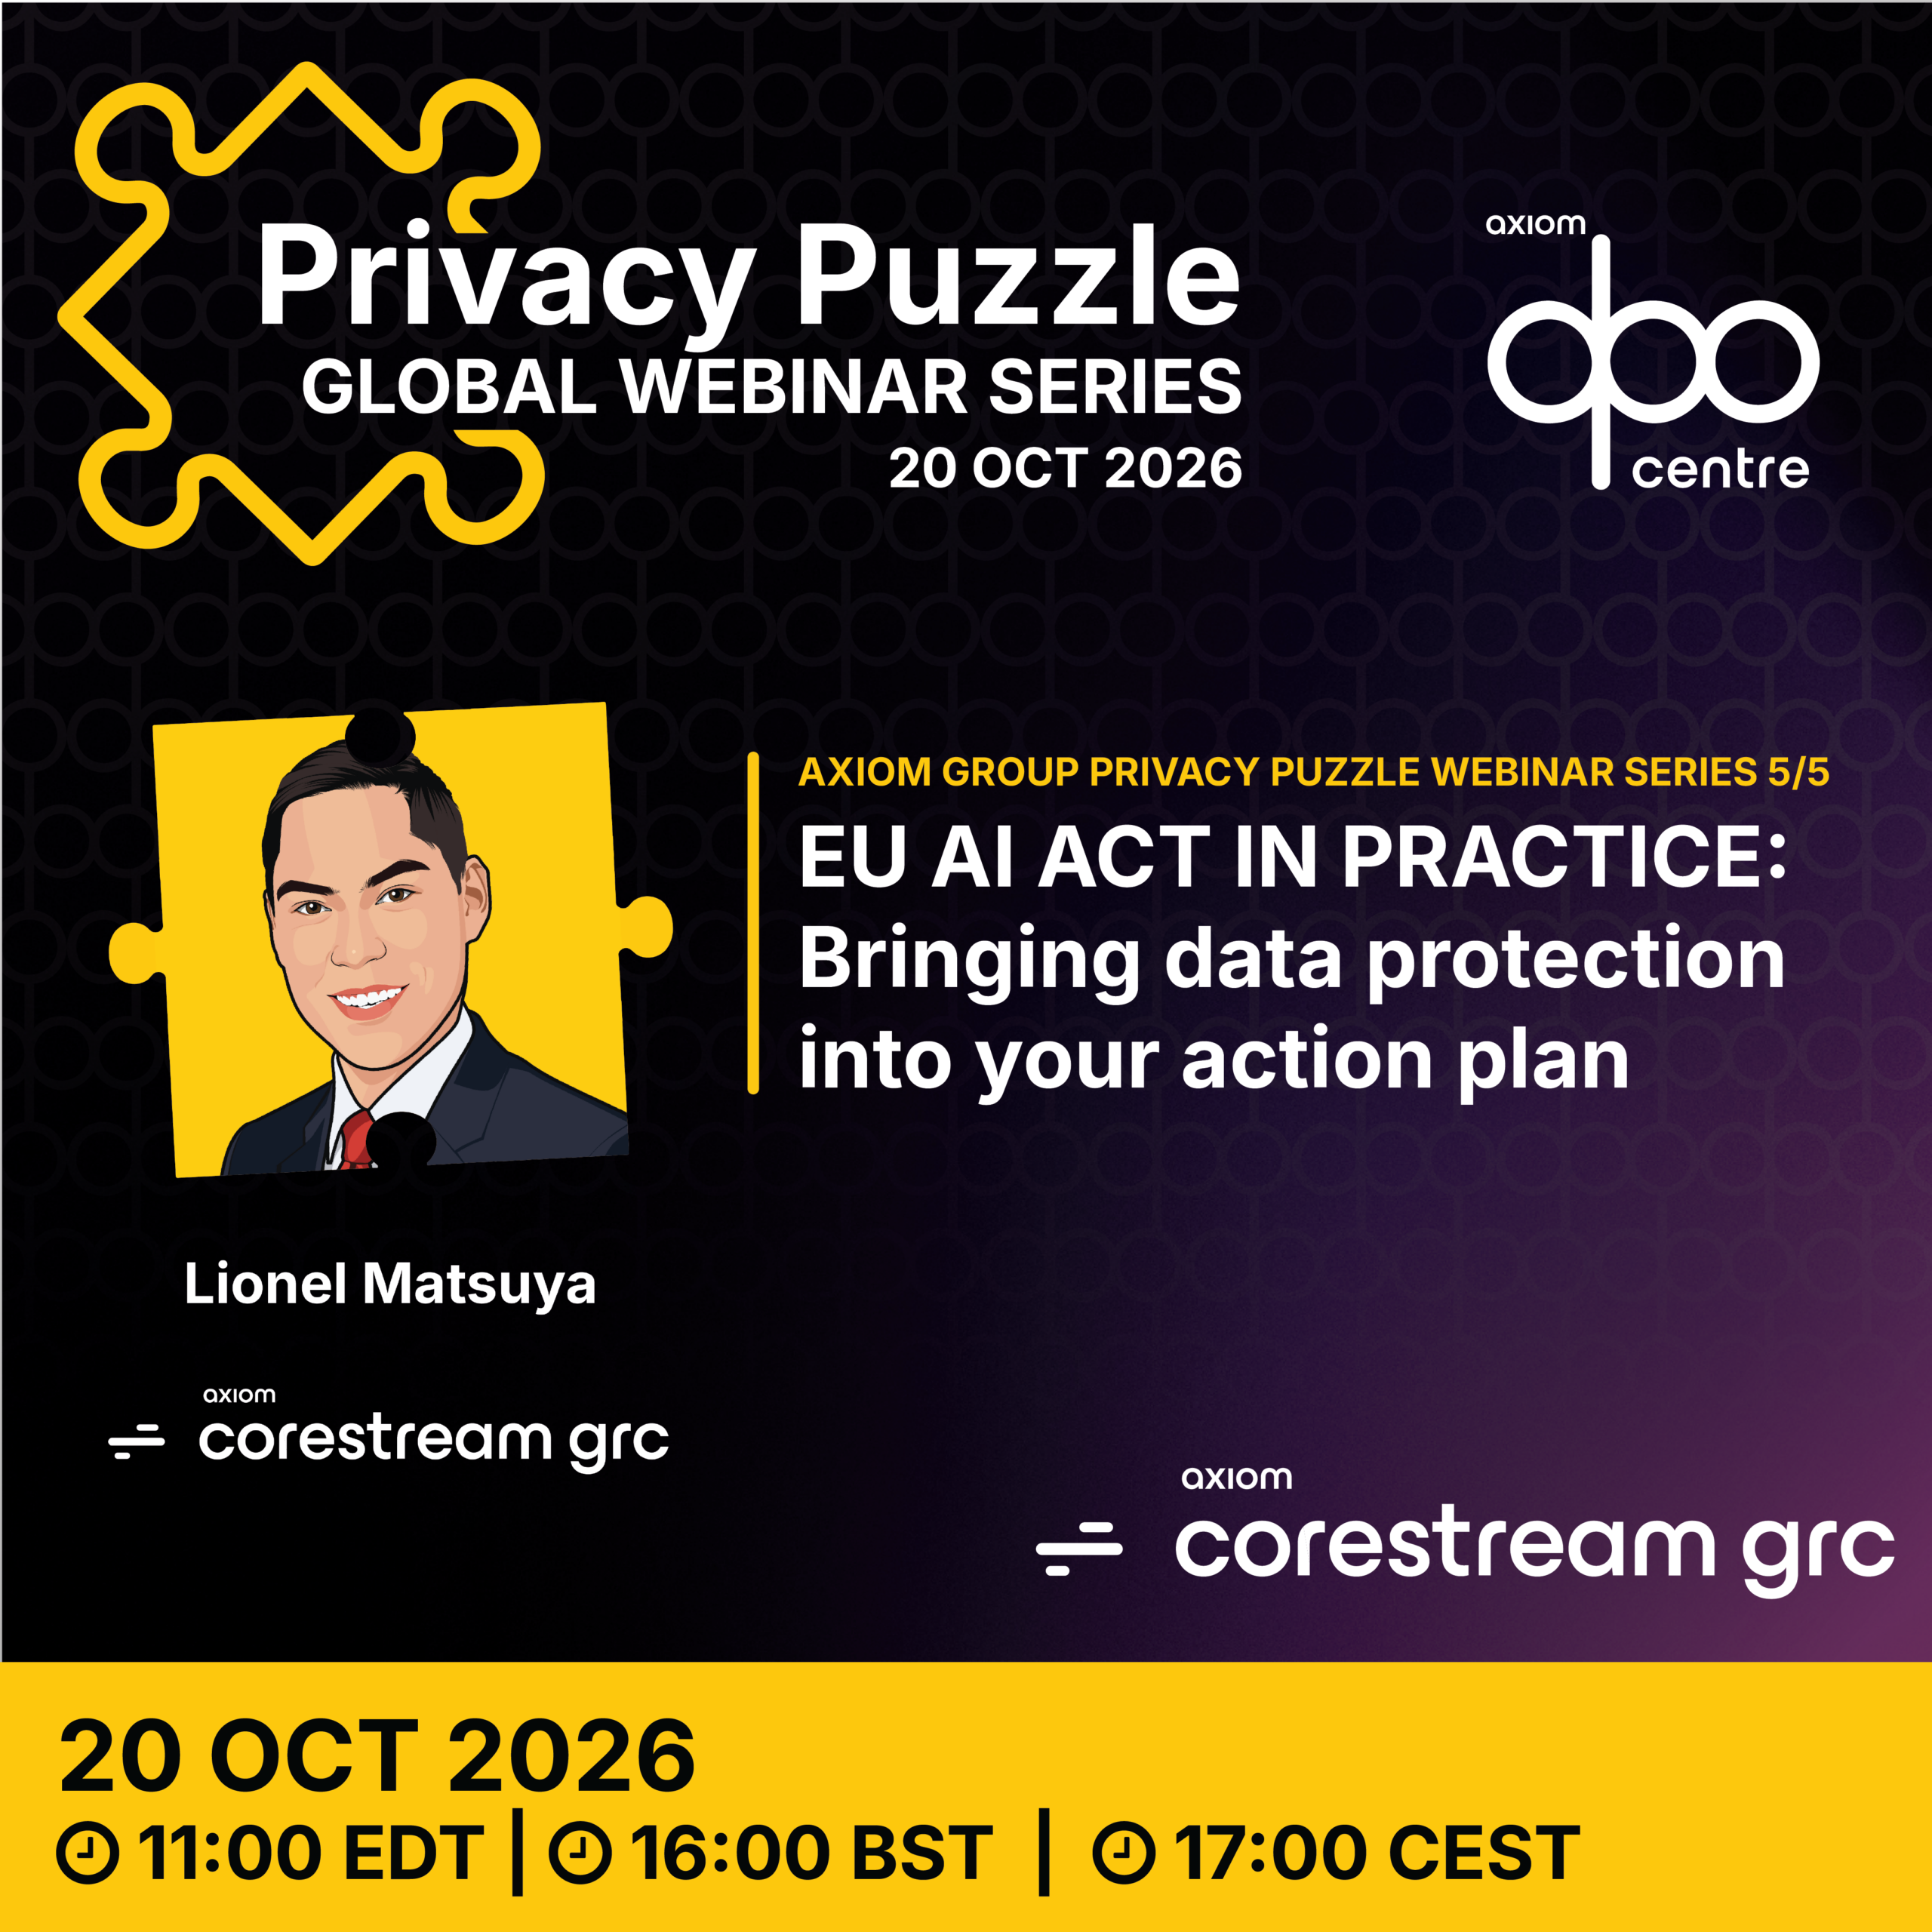
Where to start? The experts at the DPO Center and CoreStream GRC have created a webinar to discuss the EU AI Act in practice and what your company should be doing now.
If you’d like to learn how to connect AI governance, data protection and compliance into one strategy, then this webinar is for you!
Date: 20 October 2026
Time: 16:00 BST, 11:00 EDT, 17:00 CEST
What is the EU AI Act?
The EU AI Act is the first major law designed to regulate artificial intelligence:
The AI Act is “a crucial piece to putting guardrails in place. And it puts Europe in the position to shape global efforts on how to tackle” the dangers of the technology. – Ursula von der Leyen, President, European Commission
The EU AI Act takes a risk-based approach, with stricter requirements for AI systems that could have a significant impact on individuals, such as those used in hiring, healthcare, financial services, and critical infrastructure.
The Act “aims to strengthen our democracies by ensuring artificial intelligence is used transparently, responsibly, and in line with European values – protecting fundamental rights while building trust in the technologies that increasingly shape public life”.
European Commission, Official Statement on Fundamental Values
As the Act’s requirements are rolled out, organizations must demonstrate appropriate governance, oversight, risk management, and transparency. But for businesses using personal data, AI Act compliance cannot be separated from existing data protection obligations.
Why the EU AI Act matters for GRC and AI governance
With many EU AI Act provisions already in place and high-risk AI obligations set to apply from December 2027, organizations have a valuable opportunity to prepare strategically rather than reactively.
For risk and compliance leaders, the challenge isn’t simply understanding the regulation. It’s understanding how AI governance fits into existing processes, controls, risk assessments, and oversight structures.
For example:
- How does the EU AI Act affect existing compliance programs?
- Where does AI governance overlap with privacy requirements?
- What evidence will regulators expect organizations to maintain?
- How can risk and compliance teams monitor AI effectively without increasing manual workloads?
- What role should AI play in governance activities themselves?
And these aren’t future challenges, but challenges organizations are already facing today.
What you’ll learn about AI governance and EU AI Act compliance
CoreStream GRC’s Head of Client Solution Design, and former PWC leader, Lionel will explore:
- What the EU AI Act means for existing data protection and compliance programs
- Where the AI Act and existing data protection obligations overlap
- How NIST AI RMF can support AI risk assessment and ongoing governance
- Where AI can support privacy teams, and where human judgment remains critical
“A practical starting point is to create an inventory of AI systems, assign an accountable owner to each one, determine whether personal data is involved, classify the level of risk, document existing controls and identify gaps. Organizations should also define how AI systems will be monitored, how incidents will be escalated and what evidence must be retained to demonstrate that controls are operating effectively.”
Lionel Matsuya, Head of Client Solution Design, CoreStream GRC
The session will help participants move from regulatory awareness to a coordinated plan for AI oversight. Attendees will have the opportunity to put their own questions to specialists working across AI governance, data protection and GRC.
Meet the speakers
Lionel Matusya
Head of Solution Design, CoreStream GRC
With 12 years of experience from PWC, Lionel is all about designing bold, customized solutions that make clients rethink what’s possible with the CoreStream GRC platform. Lionel’s experience spans organizations of all sizes and across various levels of GRC maturity, both locally and globally. A chartered accountant with the ICAEW and a Certified Information Systems Auditor, Lionel is passionate about using technology to make people’s lives easier.
Follow him on LinkedIn here.
Michael McCagh
Data Protection Officer, DPO Centre
Michael is a highly qualified Data Protection Officer and certified AI Governance Professional. He has over 10 years’ experience advising organizations on global data protection legislation and AI compliance. Michael develops cross-jurisdictional privacy programs and governance frameworks that support innovation while managing regulatory risk. With deep expertise in the EU AI Act and emerging technologies, he helps organizations stay ahead of rapidly evolving legal and compliance expectations.
David Smith
Data Protection Officer, AI Sector lead, DPO Centre
David brings a wealth of data protection expertise, shaped by his in-depth DPO experience working across Technology and Healthcare sectors. As AI Sector Lead, he advises organizations on the responsible deployment of AI systems and compliance with global regulations. Known for his strategic approach to complex issues, David has supported high-stakes projects and contributed to national policy development within the NHS.
Aga Michalik
Data Protection Officer, DPO Centre
Aga is a CIPP/E and CIPM-certified data protection professional with strong, hands-on experience across EU data protection frameworks. She provides risk-based, business-focused advice that supports the development of effective privacy programs within global organizations. With experience in the Financial Services and Legal sectors, Aga helps organizations embed practical controls and respond to evolving regulatory expectations in a clear and scalable way.
Reserve your place
AI compliance isn’t another checkbox exercise. It’s an opportunity to build stronger governance, better oversight and a more resilient organization. The phased deadlines should not be mistaken for permission to wait. Building an AI inventory, agreeing ownership, assessing risk and establishing evidence can take time, particularly where AI is already embedded across multiple teams and suppliers. Starting now gives your organizations space to address gaps before the most demanding obligations apply.
Join CoreStream GRC and the DPO Centre to learn how leading organizations are turning AI regulation into practical business action.
Frequently asked questions about the EU AI Act and AI governance
This webinar is designed for:
GRC leaders
Compliance professionals
Privacy and data protection teams
Risk managers
Internal auditors
Legal and governance teams
Anyone responsible for AI oversight
The EU AI Act is a risk-based law for artificial intelligence. It sets different requirements according to the level of risk an AI system presents, with the strictest obligations applying to prohibited and high-risk uses.
The Act can apply to AI providers, deployers, importers, distributors, and providers of general-purpose AI models. Organizations outside the EU may also be in scope when they place AI systems on the EU market or when an AI system’s output is used in the EU.
The requirements are being introduced in phases. Prohibited-practice and general-purpose AI rules are already in effect, transparency requirements apply from August 2026, most obligations for standalone high-risk systems listed in Annex III apply from December 2027, and obligations for high-risk AI embedded in regulated products apply from August 2028.
High-risk AI includes certain systems used in areas such as employment, education, essential services, critical infrastructure, healthcare, biometrics, and law enforcement. Classification depends on the system’s purpose, context, and potential impact on health, safety, or fundamental rights.
Where an AI system processes personal data, the EU AI Act and GDPR can apply at the same time. Organizations should connect AI risk classification and oversight with existing privacy controls, including lawful basis assessments, data protection impact assessments, data minimization, transparency, security, and data-subject rights.
Depending on their role and the system’s risk level, organizations may need an AI inventory, risk assessments, technical documentation, data-governance records, testing results, human-oversight procedures, logs, incident records, supplier evidence, and ongoing monitoring. Evidence should show that controls operate in practice, not only that policies exist.
The NIST AI Risk Management Framework can help organizations structure AI governance around the Govern, Map, Measure, and Manage functions. It supports consistent risk assessment and monitoring, but it does not replace the specific legal obligations, documentation, or conformity requirements of the EU AI Act.
Start by identifying AI systems and accountable owners, determining your role for each system, classifying risk, mapping existing privacy and GRC controls, and prioritizing gaps. Build evidence collection, human oversight, supplier assurance, and monitoring into existing governance processes rather than creating a separate compliance silo.