
GRC resources
Discover blogs, news, events and more from CoreStream GRC’s experts.
-
·
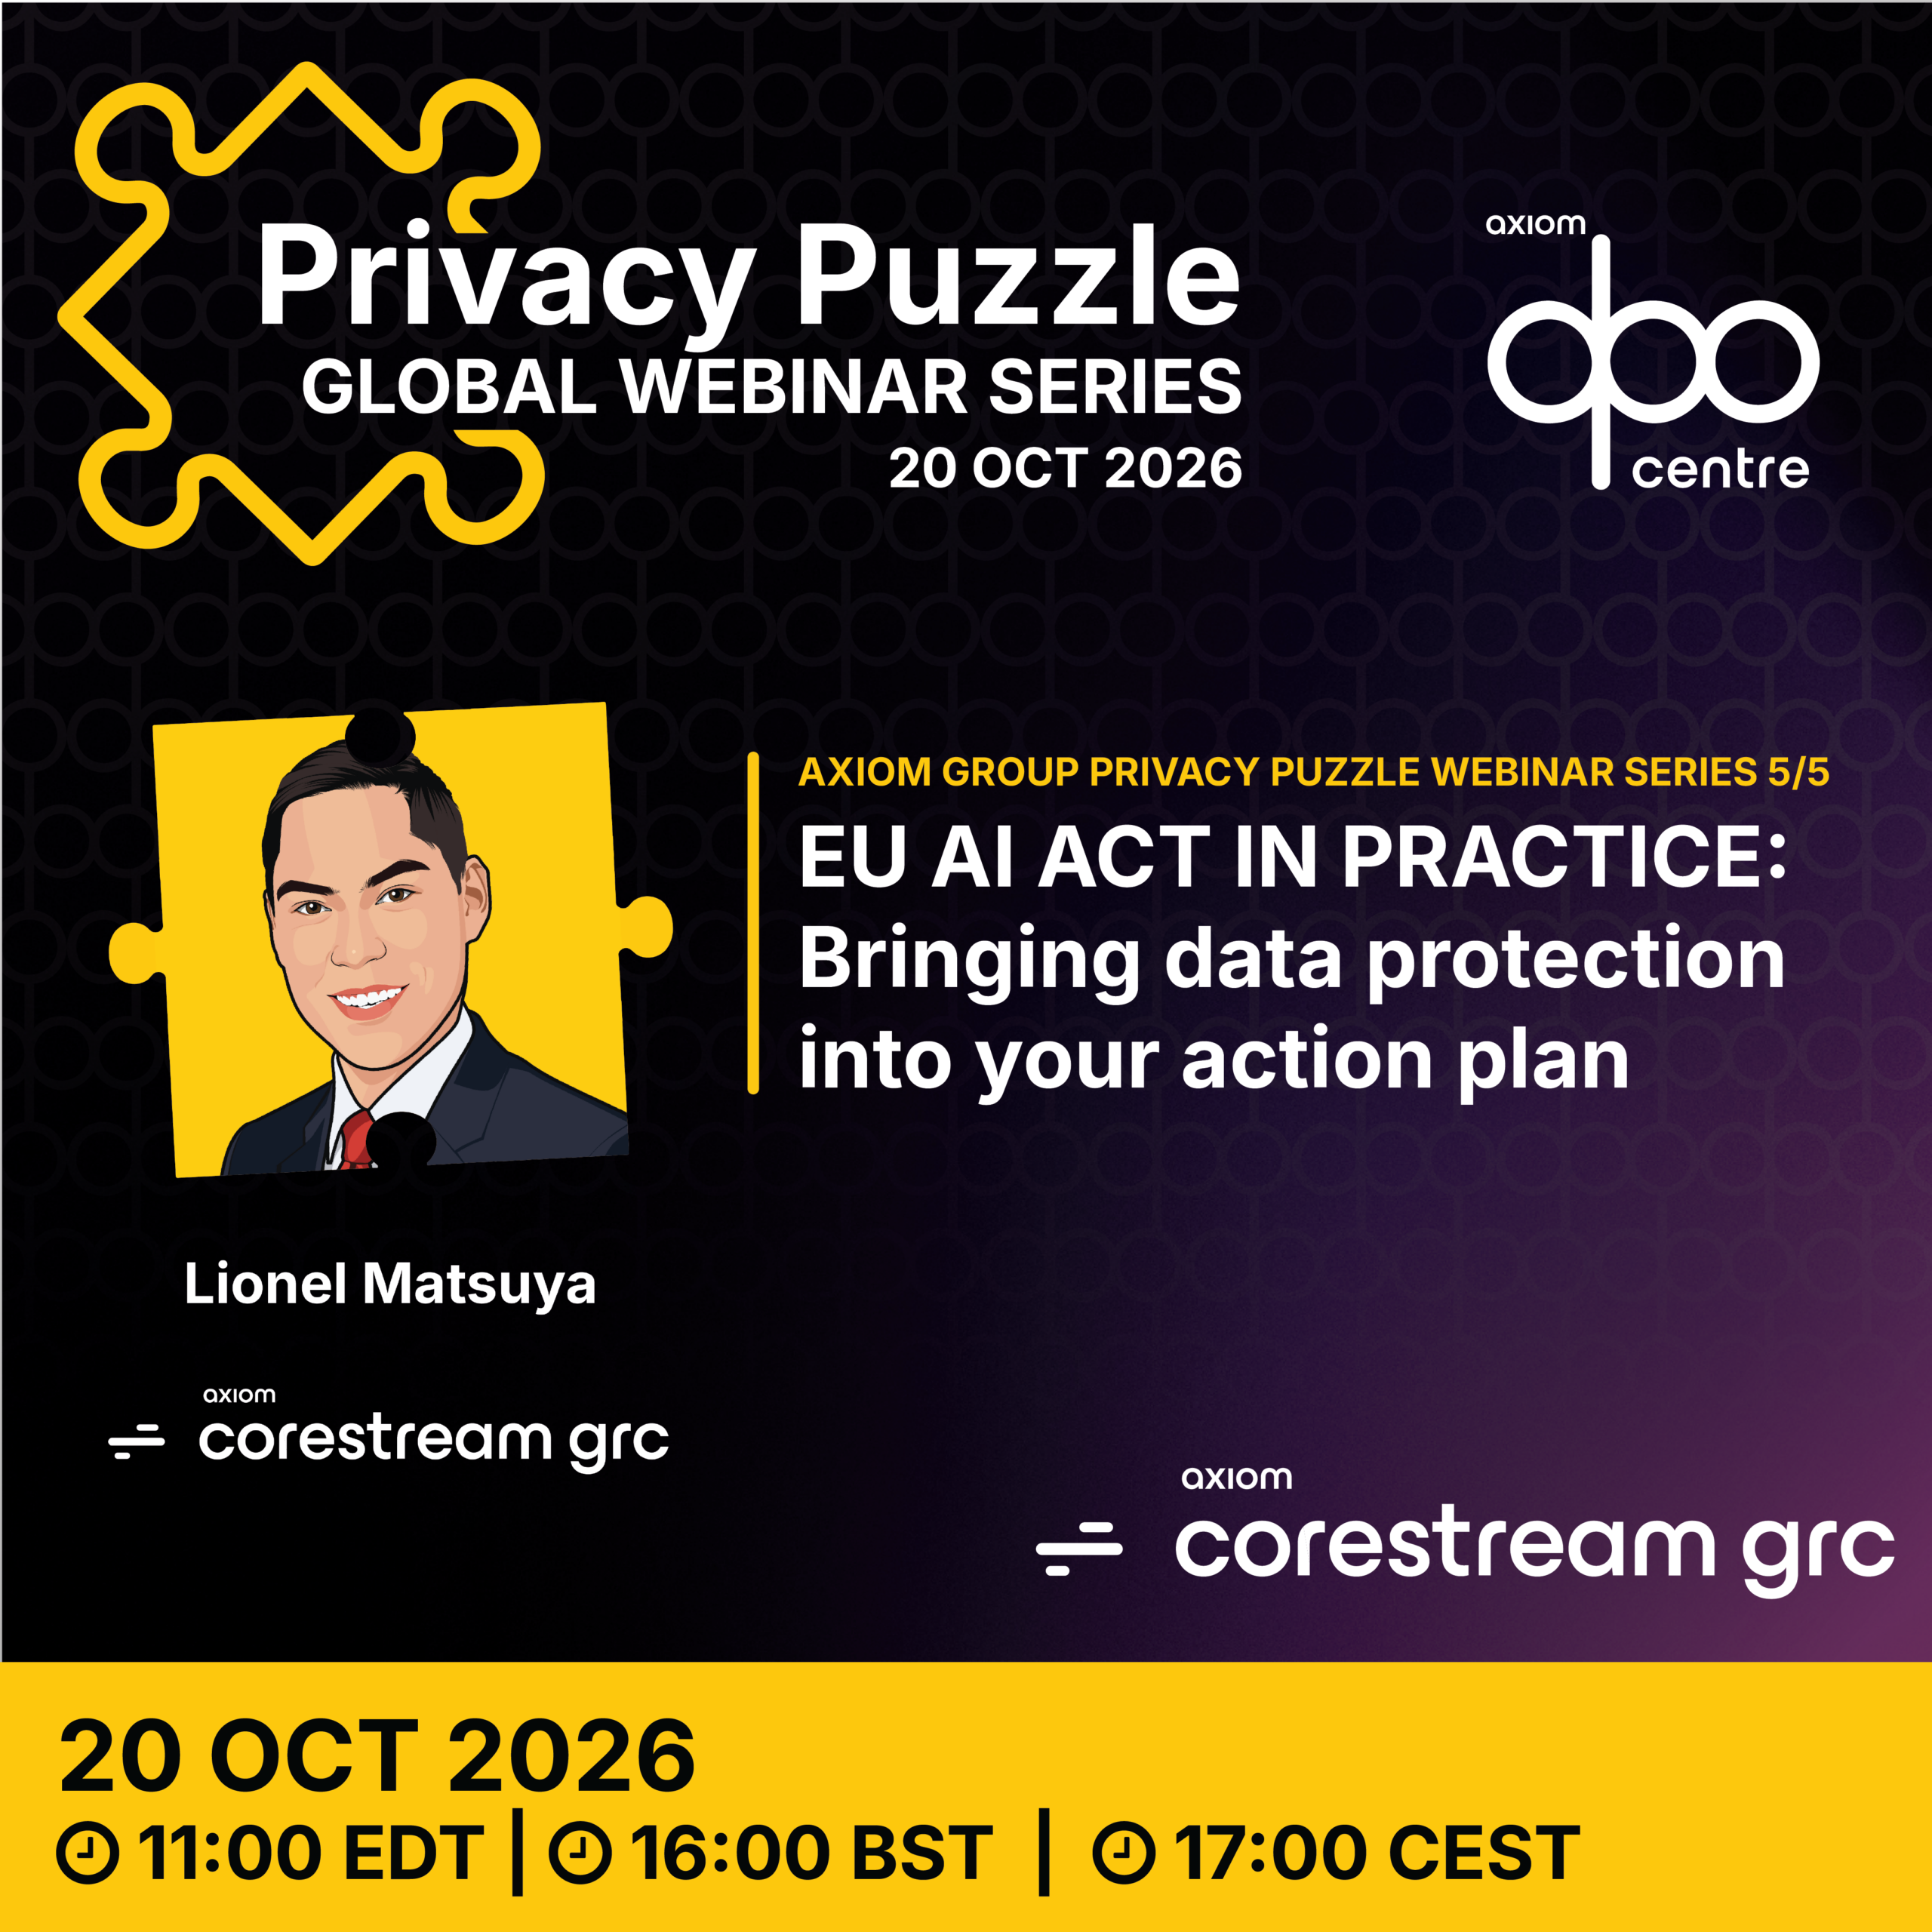
EU AI Act in practice: bringing data protection into your action plan
Most organizations are treating the EU AI Act as a standalone compliance project. That’s a mistake. If your AI systems process personal data, AI compliance doesn’t sit in its own silo. Treating these responsibilities separately risks duplicated work, inconsistent controls and gaps in accountability. Data protection, governance, risk management, audit and compliance all have a…
-
·
The ASOS breach shows why customer messaging platforms belong in your third-party risk management framework
Hackers used ASOS’s own app to announce its data breach. Here is what the attack, and the retailer’s response, teach GRC teams about third-party risk and incident response. Key takeaways from the ASOS data breach incident Introduction: the risk consequences when the breach notice comes from the attacker At around 10am on Tuesday 6 October,…
-

·
IT risk/ISO27001/NIS2/SOC 2
What is IT risk? IT risk is the risk that technology systems, data, infrastructure, people, or digital processes could fail, be disrupted, be misused, or expose the organization to harm. It includes risks linked to cybersecurity, system availability, data confidentiality, access controls, third parties, operational resilience, regulatory compliance, and technology change. In governance, risk, and…
-

·
Enterprise Risk Management (ERM) and ISO 31000
What is enterprise risk management (ERM)? Enterprise risk management (ERM) is the organization-wide process of identifying, assessing, managing, monitoring, and reporting risks that could affect strategic objectives. It gives leadership and the board a joined-up view of risk across the business, rather than leaving each function to manage risk in isolation. In governance, risk, and…
-

·
Risk assessment
What is a risk assessment? Risk assessment is the process of identifying, analyzing, and evaluating risks so an organization can understand what might affect its objectives and decide what action is needed. It helps teams work out what could happen, how likely it is, how serious the impact could be, and whether the risk sits…
-
·
Risk mitigation
What is risk mitigation? Risk mitigation is the process of reducing the likelihood or impact of a risk through controls, actions, safeguards, or changes to the way an organization operates. It is one type of risk response, alongside accepting, avoiding, sharing, or transferring risk. In governance, risk, and compliance (GRC), risk mitigation matters because identifying…
Ready to chat with our experts?
Contact us today!
This form may not be visible due to adblockers, or JavaScript not being enabled.