
GRC resources
Discover blogs, news, events and more from CoreStream GRC’s experts.
-
·
How to put objectives at the center of your risk management program
Organizations do not exist to manage risks. They exist to achieve objectives. Yet too many risk programs are still built around the risk register. Teams spend countless hours identifying, scoring, and reviewing risks, only to be left with a list of red, amber, and green ratings that offer little insight into what leaders actually need…
-
·
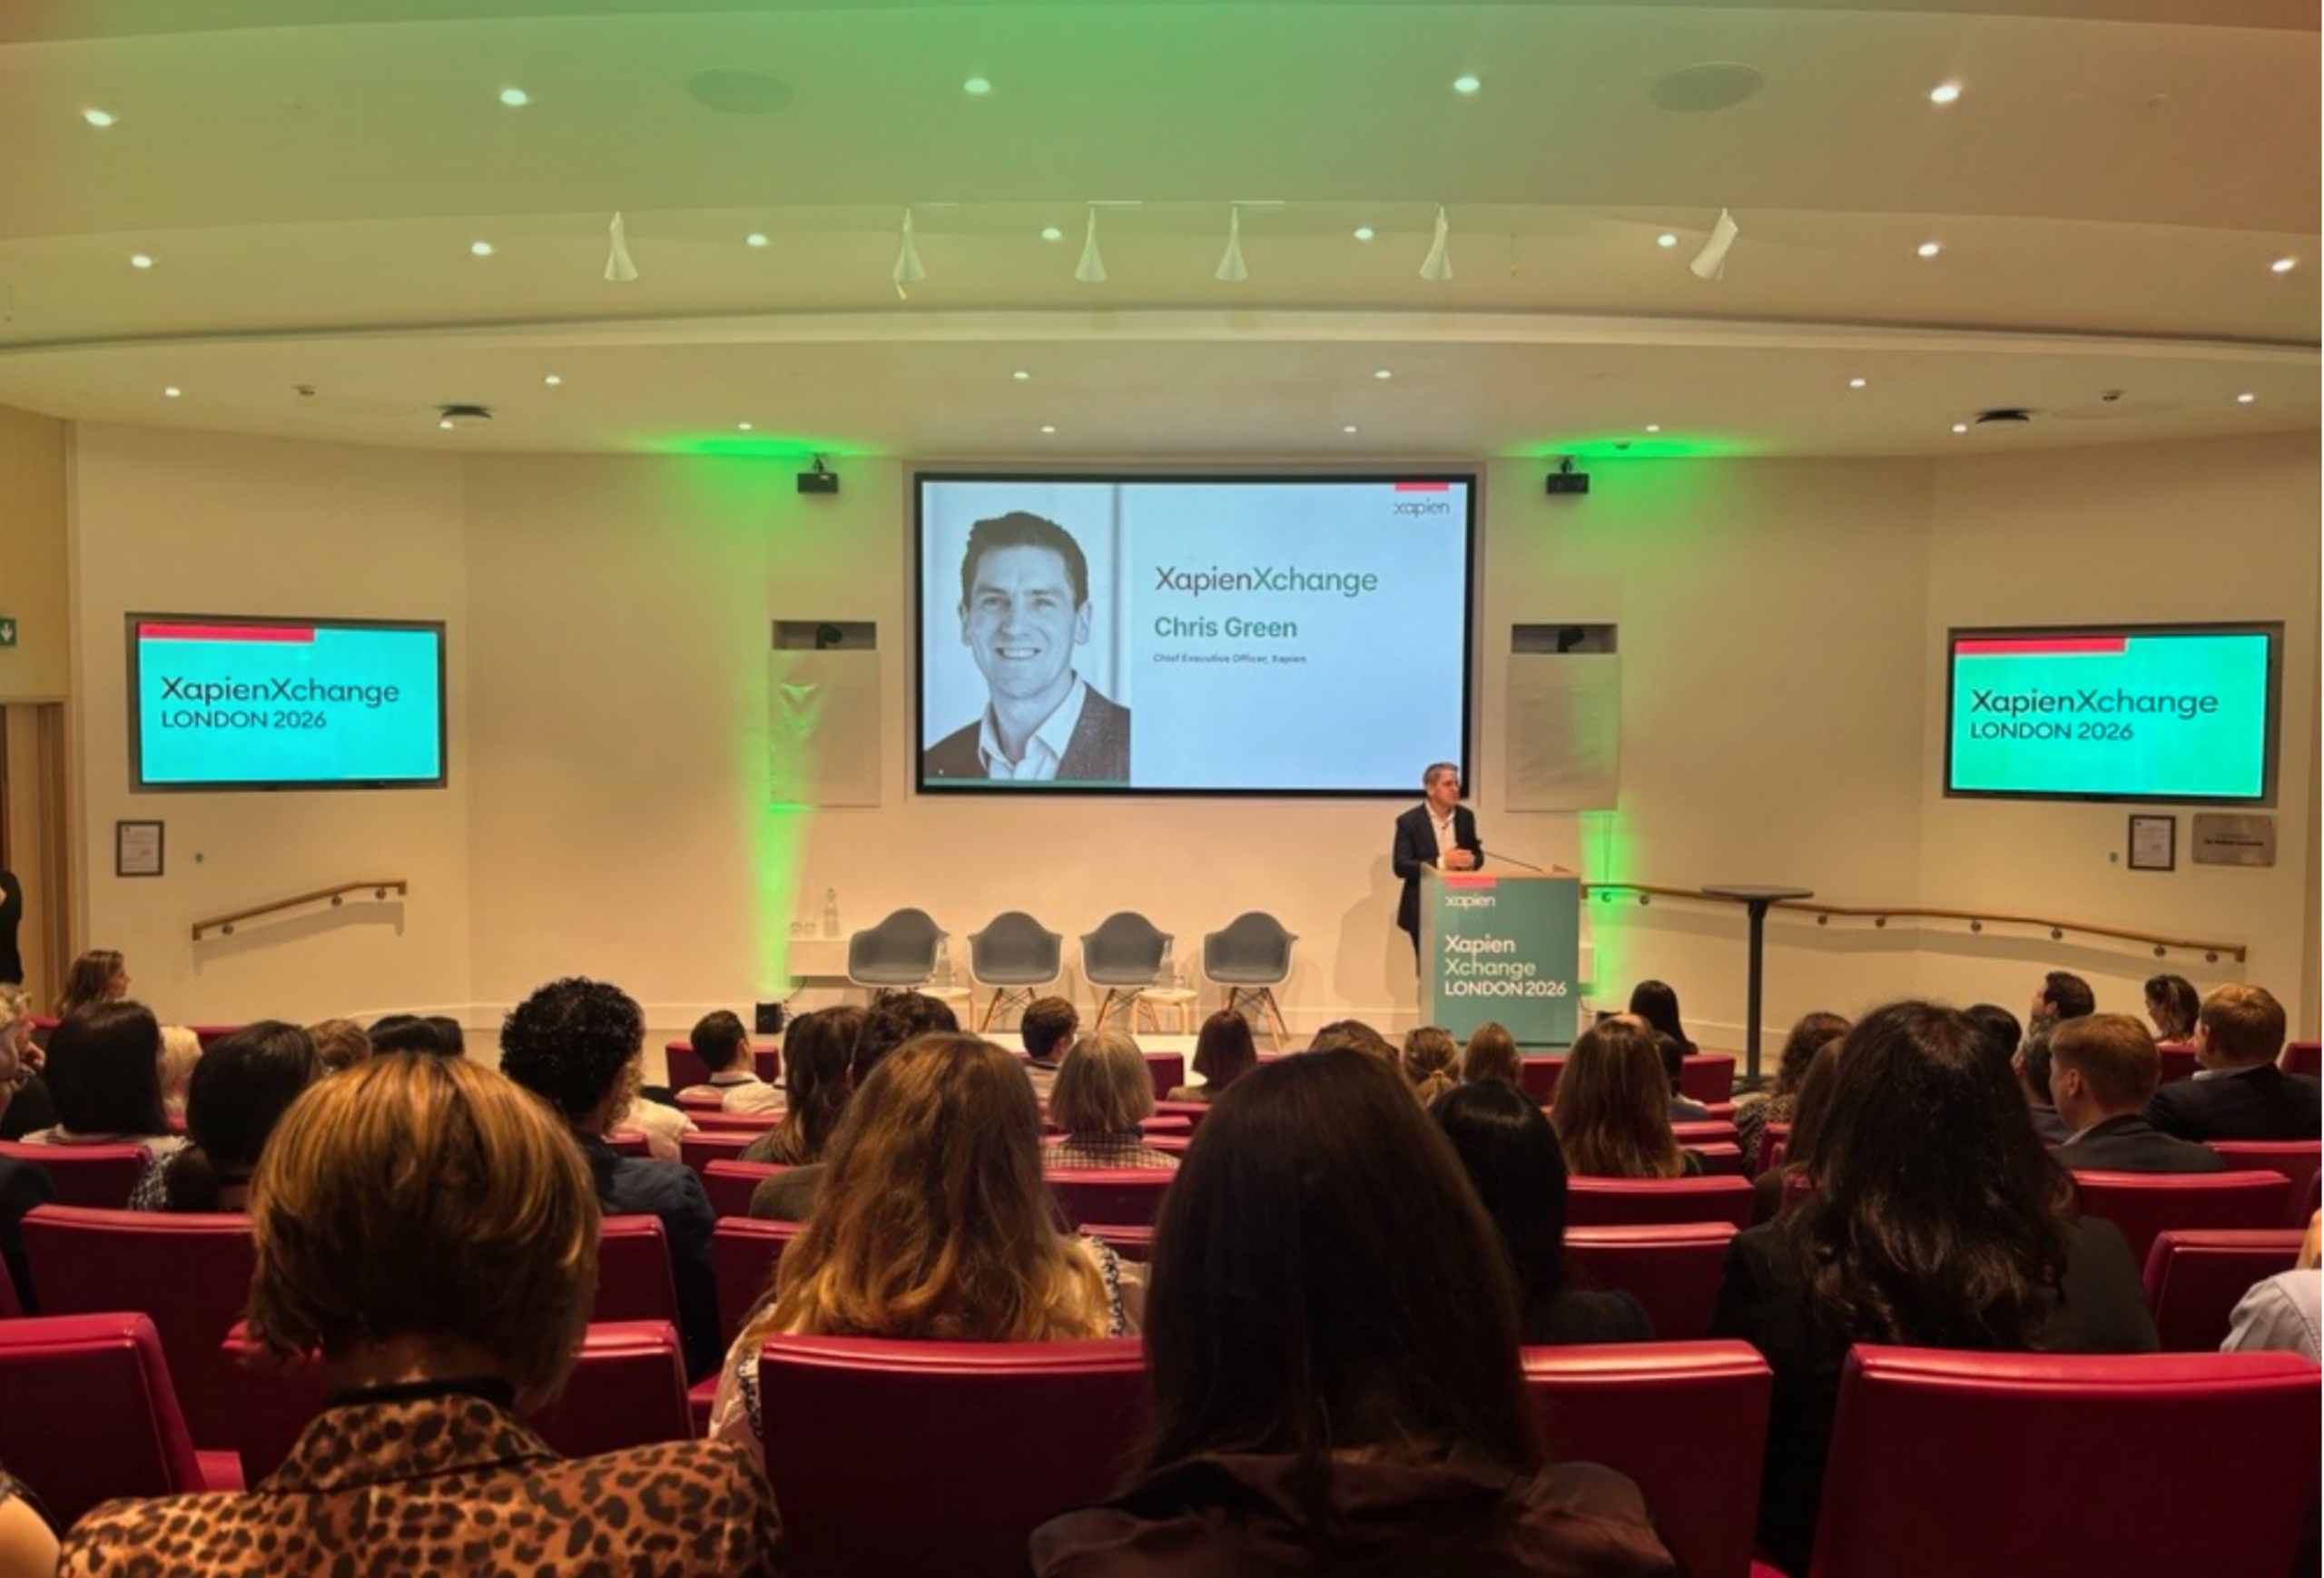
XapienConnect 2026 key takeaways: what true transformation in due diligence looks like
The end of the experimental era: what true transformation in due diligence looks like At this year’s Xapien Connect 2026, one message came through loud and clear: AI enables business transformation. For the last few years, organizations have been focused on AI experimentation. Pilot projects. Proofs of concept. Internal debates about what AI might mean…
-
·
Spotlight on Women in GRC: What global logistics teaches us about the future of compliance
Lila Landis on building compliance across 100 countries, winning stakeholder support through influence rather than authority, and ensuring GRC helps organizations move faster rather than slowing them down. In the latest Spotlight on Women in GRC podcast, host Lucy Montague speaks with Lila Landis, Global Head of Compliance at JAS Worldwide, a global freight forwarder,…
-
·
The PHP2Shell vulnerability shows why third-party risk management must move at the speed of attackers
Critical PHP vulnerabilities put most of the web at risk and left customers asking suppliers 1 question. Here’s what PHP2Shell teaches third-party risk management teams about supplier assurance. Key takeaways from the PHP vulnerability alert Introduction: “are you affected?” the question every supplier was asked In the days after 21 October, CoreStream GRC’s customer success…
-
·
Spotlight on Women in GRC: Building an effective risk culture with a Chief Risk Officer
Nadia Crawford on changing perceptions of risk, building credibility through continuous learning, and why effective risk management starts long before a decision reaches the risk team. Putting people at the heart of your risk programs Many risk leaders begin their careers in governance, compliance, or audit. Nadia Crawford’s route was different. Starting in process improvement,…
-
·
Hackers turned French supermarket fridges into ovens: who owns the risk in your building and equipment controls?
Attackers overheated fridges in hundreds of French supermarkets using flaws flagged months earlier. Here’s what it teaches risk and compliance teams about legacy equipment and supplier risk. Key takeaways from the French supermarket hack Introduction: when freezers became ovens On the morning of Monday 12 October, staff at 100s of supermarkets across France found aisles…
Ready to chat with our experts?
Contact us today!
This form may not be visible due to adblockers, or JavaScript not being enabled.