
GRC blogs
Explore our blogs for expert insights, industry updates, and practical guidance
Designed to challenge ways of thinking and help your enterprise excel in GRC.
-
Beyond the RAG chart: effective GRC reporting at board-level
Read more: Beyond the RAG chart: effective GRC reporting at board-levelKey takeaways Introduction: from static snapshot to compliance story Picture a typical quarterly board pack. The compliance slide shows 98% green, no red flags and no open questions, so the board moves on within a few minutes. Then, months later, a control failure that had in fact been recurring quietly for a year surfaces as a genuine incident, and the first question anyone asks…
-
Health compliance: how to manage HIPAA, HITRUST, AI Governance and Open Payments
Read more: Health compliance: how to manage HIPAA, HITRUST, AI Governance and Open PaymentsKey takeaways for overlapping healthcare compliance requirements in North America Introduction: why is healthcare compliance becoming harder to manage? Healthcare compliance teams are no longer managing one major requirement at a time. They are dealing with HIPAA, HITECH, HITRUST, cyber risk, AI governance, Open Payments, conflict of interest and internal oversight at once. Those expectations…
-
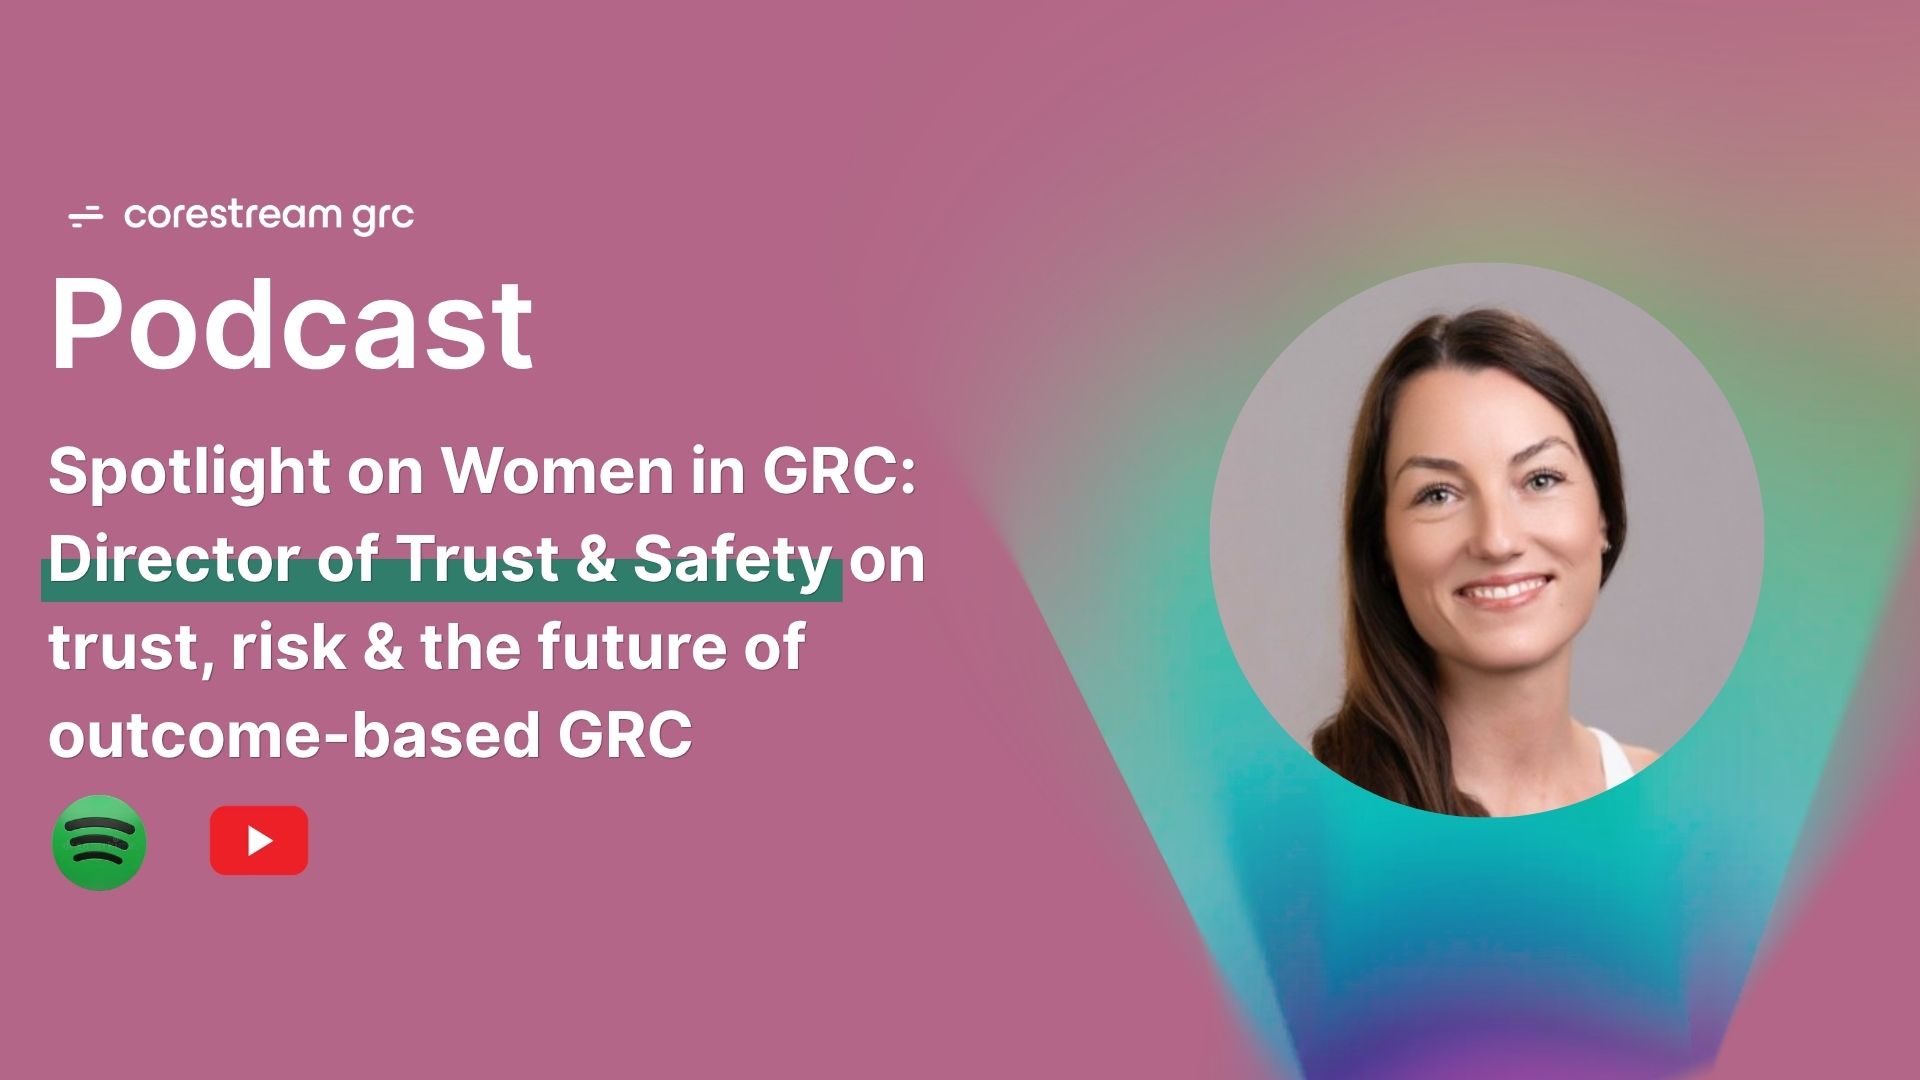
Spotlight on Women in GRC: Sophie Walsh on trust, risk, and the Future of outcome-based GRC
Read more: Spotlight on Women in GRC: Sophie Walsh on trust, risk, and the Future of outcome-based GRCIn a recent Spotlight on Women in GRC podcast, Lucy Montague sat down with Global Director of Trust & Safety, Sophie Walsh, a risk, integrity and compliance leader whose career spans charities, global technology platforms, and some of the most complex risk environments in modern business. From social care and NGOs to digital regulation and e-commerce, Sophie’s work has been guided…
-
Too much faith in frameworks: The governance limits of industry standard certifications
Read more: Too much faith in frameworks: The governance limits of industry standard certificationsKey takeaways Introduction: when GRC certification becomes destination At a recent CoreStream GRC webinar on the modern CISO’s compliance stack, the panel was asked a blunt question: are there any regulations, frameworks or certifications that organizations place too much faith in? Tom Cornelius, founder of the Secure Controls Framework and senior partner at ComplianceForge, didn’t hesitate. He named SOC 2 and ISO 27001 directly, and called the market that…
-
Spotlight on Women in GRC: Emma Price on curiosity, creativity and why value-based GRC starts with better questions
Read more: Spotlight on Women in GRC: Emma Price on curiosity, creativity and why value-based GRC starts with better questionsIn this episode of CoreStream GRC’s Spotlight on Women in GRC podcast, Lucy Montague sits down with Emma Price, Partner at Brave, former Deloitte partner and one of the UK’s leading voices in risk and resilience. With more than 25 years of experience helping boards navigate uncertainty, Emma shares: Curiosity: The skill that launched a 25-year career in GRC and a…
-
Simplifying risk in a complex world to achieve business objectives – key findings from the Spotlight on Women in GRC
Read more: Simplifying risk in a complex world to achieve business objectives – key findings from the Spotlight on Women in GRCIn this episode of CoreStream GRC’s Spotlight on Women in GRC podcast, Lucy Montague speaks with Sharon Sharples, Chief of Staff and Head of Operational Risk Governance and Insights at Barclays, about her journey from change management into risk leadership, the evolving role of GRC in modern organizations, and why curiosity, simplification, and flexibility will define the…
-
Beyond the token bill: why AI governance now means budgeting, sovereignty and capacity, not just risk
Read more: Beyond the token bill: why AI governance now means budgeting, sovereignty and capacity, not just riskKey takeaways Introduction: the hidden costs of AI for GRC teams In May, engineers at Uber found that they had spent an entire year’s AI budget in just four months. The culprit was Claude Code, rolled out enthusiastically across the organization to speed up software development. It worked. It also cost so much, so fast, that leadership had to step in and cap…
-
Spotlight on Women in GRC: Woman of the Year on intergenerational learning, AI and the future of GRC
Read more: Spotlight on Women in GRC: Woman of the Year on intergenerational learning, AI and the future of GRCIn this special episode of CoreStream GRC’s Spotlight on Women in GRC podcast, Lucy Montague speaks with Yvonne Gordon, 2026 Women in GRC Woman of the Year and Head of Compliance and Continuous Improvement, about her unconventional route into governance, risk and compliance, the importance of mentorship, and why creating opportunities for others has become her personal mission. The…
-
Spotlight on Women in GRC: DPO on GDPR, privacy culture and ESG
Read more: Spotlight on Women in GRC: DPO on GDPR, privacy culture and ESGIn this episode of CoreStream GRC’s Spotlight on Women in GRC podcast, Lucy Montague sits down with the series’ first DPO, Lorraine Pinter, to discuss her journey from law into privacy, the evolution of GDPR, building confidence as a leader, and why data protection remains one of the most impactful and personally relevant areas of GRC. The DPO’s podcast episode explores: Starting your…
-
The future of GRC: what principles-based regulation means for GRC teams
Read more: The future of GRC: what principles-based regulation means for GRC teamsKey takeaways Introduction: the GRC rulebook is getting smaller, as accountability grows Ask any compliance officer what’s changed in their job over the last two years, and few will point to a single new regulation. They will point to something harder to pin down: a growing expectation that they explain and defend their own judgment, rather than simply follow a rule written by someone…
Ready to speak to our experts?
Discover our case studies
The success stories of flexible intuitive GRC technology
-
CASE STUDY: South Western Railway
Reinventing rail compliance: how South Western Railway kept obligations under control through re-nationalization Contracts change. Ownership changes. Reporting lines change. However, what does not change is the impact risk can have on a business. Obligations must be tracked, updated, evidenced, and reported. And if your Governance, Risk & Compliance (GRC) platform cannot flex with the business change, teams fall back to outdated methods; spreadsheets, inbox chasing and hoping nothing gets missed. South Western Railway…
-
GUIDE: buying a GRC platform
How to choose the right GRC software for your business: A buyer’s guide Buying GRC software is rarely just a software decision. By the time most organizations start reviewing platforms, they are usually already dealing with something more structural: fragmented reporting, unclear ownership, too much manual chasing, weak leadership visibility, and governance activity spread across…
-
CASE STUDY: Pool Re
From constraint to control: how CoreStream GRC transformed risk management at Pool Re About Pool Re Pool Re is the UK’s largest terrorism reinsurer, trusted by over 150 insurers and globally recognized as the leading experts in terrorism risk financing. Their mission is to provide financial protection against the risk of terrorism and, in so…
Ready to upgrade your GRC tech?
Contact the team and request your demo today.
This form may not be visible due to adblockers, or JavaScript not being enabled.